Silent Lynx Targets CIS Government Organizations Using Four Malware Infection Chains
The threat actor known as Silent Lynx has been linked to a new series of cyber espionage attacks targeting government organizations across Central Asia and the Commonwealth of Independent States (CIS). Observed between June 2025 and August 2026, the campaign uses four distinct infection chains involving malicious documents, PowerShell-based downloaders, GitHub-hosted scripts, and crafted WinRAR archives.
The attacks ultimately deploy custom reverse-shell malware, including FoalShell, Chvost, Laplas, and PickleShell, giving attackers interactive remote access to compromised systems.
Cisco Talos tracks the activity as UAT-6275, while Recorded Future's Insikt Group tracks it as TAG-193. Researchers have identified victims and phishing themes across nine countries: Kazakhstan, Kyrgyzstan, Tajikistan, Turkmenistan, Uzbekistan, Armenia, Azerbaijan, Russia, and Belarus.
Who Is Silent Lynx?
Silent Lynx was first publicly documented in early 2025, when researchers reported attacks against embassies, lawyers, government-backed banks, and think tanks in Kyrgyzstan and Turkmenistan.
The group is assessed to have a Kazakhstan nexus and has been active since at least 2020. Researchers have identified potential overlaps with several other threat clusters, including YoroTrooper, Comrade Saiga, ShadowSilk, Cavalry Werewolf, and Tomiris.
However, researchers have not observed direct indicators or toolset overlap establishing that UAT-6275 and YoroTrooper are the same group.
Comrade Saiga and Hydra Saiga refer to the same threat actor. Research into Hydra Saiga has highlighted its focus on infrastructure associated with water resources in Central Asia, using custom implants written in Rust, Go, and Python alongside living-off-the-land techniques.
Spear-Phishing Campaigns Target Government Officials
Silent Lynx relies on spear-phishing emails designed to appear relevant to government and diplomatic activities. The messages use official-looking documents and themes involving international relations, trade, energy, and aviation to increase the likelihood that recipients will open malicious attachments.
Researchers identified at least eight campaigns across the region between January 2025 and May 2026.
Some of the identified lures included:
- A diplomatic letter addressed to Armenia's Ministry of Foreign Affairs.
- A Turkmenistan airspace application form.
- A business proposal concerning Russia's Orsk Oil Refinery.
The phishing emails were reportedly sent from compromised government accounts, making them appear more credible to recipients. By abusing legitimate accounts and using regionally relevant documents, the attackers attempted to exploit existing trust between government organizations and their contacts.
Four Infection Chains Used to Deploy Malware
Cisco Talos identified four distinct infection pathways associated with UAT-6275.
1. Malicious Word Documents
In June 2025, the attackers used macro-enabled Microsoft Word documents to download and execute a second-stage binary. This approach relies on malicious document content to initiate the infection and retrieve additional payloads.
2. PS2EXE-Based Downloaders
In July 2025, the group used downloaders packaged with PS2EXE, a utility that converts PowerShell scripts into Windows executables.
These downloaders retrieved reverse-shell payloads and created scheduled tasks to maintain persistence on compromised systems.
3. Malicious LNK Files and GitHub-Hosted PowerShell
In October 2025, the attackers distributed RAR archives containing malicious Windows shortcut files, or LNK files.
Opening the shortcut launched PowerShell, which retrieved and executed a script hosted on GitHub. The script provided remote shell access to the compromised machine.
Later versions of this infection chain also downloaded PickleShell and placed it in the Windows Startup folder, allowing the malware to launch automatically whenever the affected user logged in.
4. WinRAR Exploitation
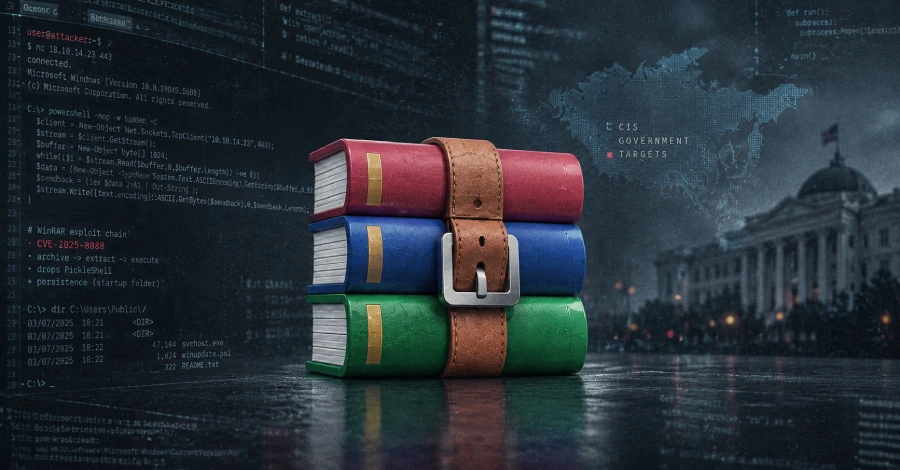
In April 2026, the group adopted a more advanced delivery method by using a crafted RAR archive that exploited CVE-2025-8088, a WinRAR vulnerability.
The archive was used to drop PickleShell into the Windows Startup folder, enabling the malware to execute during subsequent user logins.
This campaign marked the first identified instance of UAT-6275 weaponizing a software vulnerability as part of its malware delivery process.
Custom Reverse Shells Enable Remote Access
The attacks deploy several custom reverse-shell tools, including FoalShell, Chvost, Laplas, and PickleShell.
Reverse shells allow an attacker to establish an interactive command channel with a compromised system. Depending on the implementation and the attacker's privileges, this access can support remote command execution, further reconnaissance, and the deployment of additional tools.
The use of multiple infection chains and custom payloads suggests that the group adapts its delivery methods to different targets and operational requirements.
The repeated use of scheduled tasks, Startup-folder persistence, PowerShell, and publicly accessible code-hosting services also demonstrates how the attackers combine conventional malware delivery with techniques that may blend into legitimate system activity.
Fortinet FortiWeb Exploit Appears in Staging Infrastructure
Researchers also identified three publicly accessible staging directories linked to the threat actor. These directories hosted Linux-compatible tools and a publicly available proof-of-concept exploit for CVE-2025-25257, an SQL injection vulnerability affecting Fortinet FortiWeb.
The presence of this exploit suggests a possible expansion of the group's operational capabilities. However, the availability of proof-of-concept code in the staging infrastructure does not by itself establish that Silent Lynx successfully exploited FortiWeb devices in these campaigns.
Regional Espionage and Infrastructure Risks
The group's targeting patterns indicate a sustained interest in government organizations across Central Asia and the broader CIS region. Environmental agencies, economic ministries, diplomatic institutions, and energy-related organizations can hold information valuable to regional intelligence operations.
The combination of compromised government email accounts, tailored phishing documents, multiple malware delivery methods, and vulnerability exploitation allows Silent Lynx to pursue access through different routes.
Cisco Talos warns that the group's continued activity and adoption of new techniques suggest it may continue targeting government organizations across the region.
Security Recommendations
Organizations in potentially affected sectors should strengthen defenses against the techniques observed in these campaigns:
- Secure government email accounts: Enforce multifactor authentication, monitor suspicious sign-ins, and investigate unexpected messages sent from legitimate organizational accounts.
- Restrict macro execution: Block macros from untrusted documents and apply appropriate protections to files received through email.
- Inspect archives and shortcuts: Treat unexpected RAR archives and LNK files with caution, particularly when they arrive with diplomatic, financial, or government-related themes.
- Monitor PowerShell activity: Look for suspicious script execution, unexpected downloads from GitHub, and commands initiated by document readers or shortcut files.
- Review persistence mechanisms: Investigate unexpected scheduled tasks and unfamiliar executables in Windows Startup folders.
- Patch vulnerable software: Update WinRAR and Fortinet FortiWeb according to their respective security advisories.
- Search for indicators of compromise: Use threat-intelligence indicators published by Cisco Talos and Recorded Future to review endpoint, email, and network telemetry.
The Silent Lynx campaign highlights the continued evolution of regional cyber espionage operations. By combining targeted social engineering, custom reverse shells, legitimate software utilities, and vulnerability exploitation, the group has expanded its methods for gaining and maintaining access to government systems.