Telegram Desktop Flaw Could Hide JavaScript in Exported Chat Files
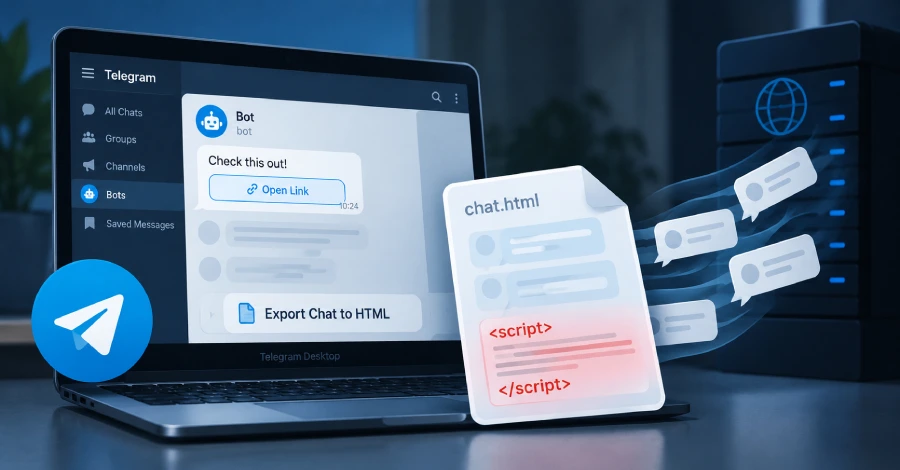
A security flaw in Telegram Desktop allowed malicious bots to hide JavaScript inside chat messages. When users exported affected chats as HTML files and opened those files in a web browser, the hidden script could run automatically.
Security researchers Denis Rostilov and Aleksander Rostilov from ExPatch disclosed the issue in a report published on September 12, 2026.
The vulnerability could allow an attacker to read messages stored in an exported HTML file, send the information to an external server, or replace the content of the exported page with a fake interface.
How the Vulnerability Worked
Telegram Desktop allows users to export individual chats or entire accounts as HTML pages that can be opened in a browser.
Bots can attach buttons to messages using Telegram’s inline keyboard feature. Before the vulnerability was fixed, Telegram Desktop inserted the text of these buttons into exported HTML files without properly escaping it.
HTML escaping ensures that characters such as < are displayed as text rather than interpreted as code.
Although Telegram escaped message text, sender names, and other fields, the researchers found that inline keyboard button text was not handled correctly.
A malicious bot could place a JavaScript payload inside a button’s text. By adding invisible characters, the button could appear empty or harmless in the Telegram Desktop application.
When the chat was later exported to HTML and opened in a browser with JavaScript enabled, the hidden script could execute without requiring another click.
Malicious Messages Could Spread Through Forwarding
The researchers found that the malicious bot did not necessarily need to be a member of the targeted chat.
A bot message containing only web-link buttons retained those buttons when forwarded. As a result, a user could unknowingly forward the malicious message into a group, where it would remain in the chat history until deleted.
The message could then be exported months or years later, allowing the payload to remain hidden for an extended period.
The researchers said they tested the issue only on their own accounts and test groups. They did not claim that the vulnerability had been exploited against real users.
Information That Could Be Stolen
When an affected HTML export was opened, the JavaScript could read the messages contained in that file and send them to an attacker-controlled server.
Potentially exposed information included:
- Message text.
- Sender names.
- Message timestamps.
- Chat name and type.
- Chat member count.
- The local path of the exported file.
Telegram Desktop divides large HTML exports into separate files containing up to 1,000 messages each. Therefore, the script could access the contents of the specific file that was opened, rather than automatically accessing an entire chat or Telegram account.
Exported Pages Could Be Replaced
The script could also modify the appearance and content of the exported HTML page.
In the researchers’ demonstration, the original export was replaced with a fake Telegram verification form. An attacker could potentially alter message dates, sender names, or message text displayed in the exported file.
However, the flaw did not modify Telegram’s original copy of the conversation or the HTML file stored on disk. It changed the page after the file was opened in a browser.
Conditions Required for Exploitation
The attack required three conditions:
- The HTML export had to be created using a Telegram Desktop version released before the fix.
- The malicious message had to be included in the exported chat or account data.
- The exported HTML file had to be opened in a browser with JavaScript enabled.
The researchers examined only Telegram Desktop’s HTML export feature. They did not report whether the JSON export format or export features in Telegram’s other applications were affected.
The contents of a full-account export also depend on how the export is configured. A single-chat export includes messages from all participants, while a default full-account export may include only the account owner’s messages in groups and channels. One-to-one chats and bot conversations can include all messages.
Telegram Released a Fix
Telegram Desktop developer John Preston added the missing HTML escaping in commit 8457d13a.
The fix was introduced in the 6.9.4 beta release on July 3, 2026, and reached the stable 7.0.1 release on July 14, 2026.
Affected Versions
- Affected: Telegram Desktop 4.15.1 through 6.9.3.
- Fixed: Telegram Desktop 6.9.4 beta, 7.0.1 stable, and later versions.
The researchers said the vulnerable code had been present in stable releases since version 4.15.1, released in March 2024.
Users should update Telegram Desktop to version 7.0.1 or later. Users on the beta channel should install version 6.9.4 or later.
Previously exported HTML files created with vulnerable versions should be exported again after updating. If an old export must be opened, users should disable JavaScript in the browser first.
Older HTML exports should be treated as untrusted, especially when they contain messages from large groups where the source of each message may be difficult to verify.
No CVE or Official Security Advisory
As of September 14, 2026, Telegram had not published specific guidance for users who still held older HTML exports.
The release notes for Telegram Desktop 6.9.4 and 7.0.1, the application changelog, and Telegram’s update announcement did not specifically mention the security fix. The Telegram Desktop GitHub repository also listed no security advisory for the issue.
The flaw had no assigned CVE identifier as of the same date.
The researchers rated the vulnerability 8.2 out of 10 under the CVSS 3.1 scoring system.
According to the researchers, Telegram confirmed the vulnerability on July 1 and offered a $500 bug bounty. They declined the payment and asked that it be donated to charity.
The researchers requested coordinated disclosure and waited until after the patch was released before publishing their findings on September 12.
Telegram’s published bug bounty rules state that vulnerabilities disclosed publicly before they are fixed are not eligible for a bounty. The rules do not clearly explain whether publication after a fix affects eligibility.
Security Recommendations
Telegram Desktop users should:
- Update to version 7.0.1 or later.
- Re-export chats that were previously saved as HTML using an affected version.
- Avoid opening old HTML exports with JavaScript enabled.
- Treat HTML exports from large groups as untrusted files.
- Avoid creating new HTML exports until the application has been updated.
The vulnerability affects the exported HTML file, not Telegram’s original cloud-stored chat history.