Critical Xen Hypervisor Vulnerabilities Allow Guest VMs to Access Other Virtual Machines' Memory
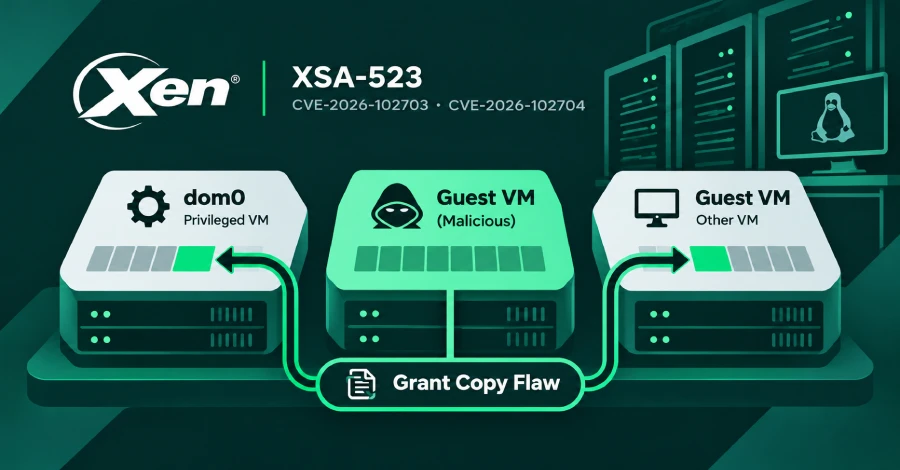
Cybersecurity researchers have disclosed two critical security vulnerabilities in the Xen hypervisor that could allow a malicious guest virtual machine (VM) to read and modify the memory of other virtual machines running on the same host, including the privileged management domain known as dom0.
The Xen Project published an advisory on November 3, 2026, confirming that patches are available but no known mitigation exists for the vulnerabilities.
Tracked as CVE-2026-102703 and CVE-2026-102704, the flaws affect all Xen versions from 4.6 onward. Versions 4.5 and earlier are not affected. Both vulnerabilities are documented under Xen security advisory XSA-523.
Dom0 is the management virtual machine that typically has extensive permissions and controls the other virtual machines on a Xen host. Compromising its memory could therefore put the entire virtualization environment at risk.
Vulnerabilities Discovered Using Anthropic's Claude Model
The Xen Project credited AI company Anthropic with discovering the vulnerabilities using its Claude model.
Stephan Lipp of Ada Logics subsequently validated the findings, while the CodeAnt AI Security Research Team independently reported the same issue.
The vulnerabilities are related to Xen's grant copy mechanism, which allows data to be transferred between virtual machines.
Each VM specifies which of its memory pages other virtual machines are permitted to access. Xen is responsible for checking these permissions before allowing memory operations.
To improve performance when processing multiple copy operations within the same memory page, Xen reuses permission checks that have already been performed. However, in certain situations, the hypervisor failed to repeat the checks when necessary.
This validation error could allow a malicious guest VM to access memory outside its permitted boundaries, including reading and writing memory belonging to other virtual machines.
Potential Impact on Virtualization Platforms
XCP-ng, an open-source virtualization platform built around Xen, warned that a single compromised guest VM could escape its isolation and potentially take control of the entire host.
The Xen advisory does not disclose any known exploitation in the wild. It also does not specify the exact level of access an attacker must obtain within a guest VM before exploiting the vulnerabilities.
Because all Xen versions from 4.6 onward are affected, other virtualization products built on vulnerable Xen releases may also be exposed until their vendors provide the necessary security updates.
Qubes OS Also Affected
Qubes OS, a security-focused operating system that uses Xen to isolate applications and workloads into separate compartments called qubes, confirmed that all supported releases and configurations are affected.
The project's security bulletin identifies Qubes OS 4.3 as the supported release requiring the fix.
Users must install the updated Xen packages, version 4.19.6-3, in dom0 and restart dom0 to apply the security update.
Users running Anti Evil Maid must also reseal their secret passphrase because the updated Xen binaries change PCR18 and PCR19.
Qubes advised users to continue installing updates normally. At the time of its November 3 announcement, the fixed packages were available in the security-testing repository and were expected to move to the stable repository following community testing over the next two weeks.
Xen Security Patches and Platform Updates
The Xen Project and affected platform vendors have published the following update information:
- Xen source: The advisory provides patches covering xen-unstable and supported branches from Xen 4.17 through 4.19.
- Xen 4.6 to 4.16: The advisory does not provide patches for these older versions. Xen 4.16 security support ended on December 2, 2024.
- XCP-ng 8.3: The fixed package is
xen-4.17.7-4.2.xcpng8.3, released November 3. Administrators must reboot affected hosts after installing the update. Vates has classified the impact as Critical. - Qubes OS 4.3: Install Xen package version
4.19.6-3in dom0 and restart the management domain. Anti Evil Maid users must additionally reseal their secret passphrase.
Debian's security tracker also listed the Xen package as vulnerable in its Bookworm, Trixie and Forky releases as of November 4, 2026, while the Sid release was listed as fixed.
Recommended Actions for Administrators
Organizations operating Xen-based virtualization environments should take the following steps:
- Identify all hosts running Xen versions 4.6 or later.
- Check vendor security advisories for the affected virtualization platform.
- Install the appropriate XSA-523 security patches as soon as they become available.
- Reboot affected Xen hosts or restart the relevant management domain as required.
- Verify that the updated hypervisor packages are installed and running.
- Review guest VM isolation and access controls, particularly for environments hosting untrusted workloads.
Administrators using older Xen versions without available security patches should evaluate their exposure and consider upgrading to a supported release.
Separate From Earlier Xen Grant Copy Vulnerability
XSA-523 is separate from XSA-500, an earlier grant copy vulnerability disclosed by the Xen Project on July 28, 2026.
Although both security advisories involve Xen's grant copy functionality, XSA-523 addresses a separate set of vulnerabilities and requires its own security patches.
The latest findings highlight the security risks associated with hypervisor memory isolation. A flaw in this layer can undermine the separation between virtual machines and potentially expose the entire host infrastructure to compromise.