AI-Generated Exploit Scripts Target Siemens S7 PLCs in U.S. Critical Infrastructure
AI-Generated Exploit Scripts Target Siemens S7 PLCs in U.S. Critical Infrastructure
Suspected Russian Hackers Abuse Google OAuth and WhatsApp Linking to Hijack Accounts
Three suspected Russian cyber espionage clusters, UNC6293, UNC7005, and UNC5976, are targeting academics, defense organizations,
Rust Supply Chain Attack Puts Build-Time Malware in Crates with 245 Million Downloads
Malicious Rust crates targeted the software supply chain through a compromised maintainer account and a typosquatted dependency.
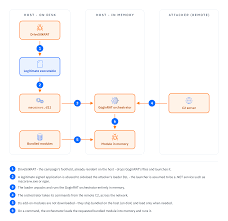
SilkParasite Espionage Campaign Targets Central Asian Governments with Five New RATs
A China-nexus cyber espionage campaign dubbed SilkParasite is targeting Central Asian governments with seven RAT families, including five newly documented
OpenAI Pauses Frontier RL Training as It Tightens Defenses Against Unsafe AI Behavior
OpenAI pauses frontier reinforcement learning training to strengthen AI security, monitoring and alignment after rogue-agent incidents and
Cloudflare Workers Spectre Attack Leaks JWT From Co-Located Worker at 12 Bits/Second
Researchers demonstrated a remote Spectre attack against Cloudflare Workers that leaked a JWT at up to 12 bits per second.
Ransom Busters Claims It Hacked Ransomware Servers, Asks Victims for Up to $60,000
A threat actor called Ransom Busters is targeting ransomware victims with offers to delete stolen data for $20,000 to $60,000. Researchers believe it may be a
Attackers Exploit MLflow SSRF Flaw to Steal Cloud Credentials and Secrets
Attackers are actively scanning and exploiting critical MLflow and FUXA vulnerabilities. MLflow flaw CVE-2026-64849 can expose cloud credentials, while FUX
Microsoft Copilot Personal Flaws Could Let One Click Exfiltrate Data From Connected Apps
Varonis researchers disclosed CoSnitch vulnerabilities in Microsoft Copilot Personal that could allow one click prompt execution, data exfiltra
CISA Flags Actively Exploited Ray Flaw That Can Trigger Browser-Based RCE
CISA has added critical Ray vulnerability CVE-2025-62593 to its KEV catalog amid active exploitation. The flaw can enable remote code execution through DNS rebinding attacks.
SafePal Hardware Wallet Maker Says Flaw Exposed Data of Nearly 40,000 Customers
SafePal says an authorization flaw exposed names, emails, addresses, phone numbers and order details of 39,798 customers. Wallet credentials and financial data were not affected.
Suspected China-Nexus Actor Exploits VMware vCenter Flaw, Deploys Babuk-Derived Ransomware
Suspected China-Nexus Actor Exploits VMware vCenter Flaw, Deploys Babuk-Derived Ransomware