Suspected ShinyHunters Member "Rey" Detained in Jordan, Reportedly Cooperating With FBI
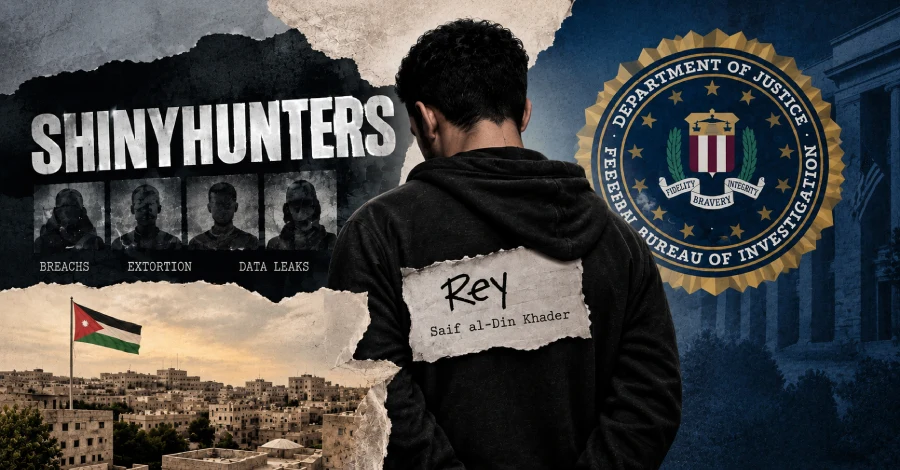
A suspected member of the ShinyHunters cybercrime group, known online as "Rey" and "ReyXBF," has reportedly been detained in Jordan and is said to be cooperating with the FBI to help identify other members of the group. Reuters reported the development on October 3, citing three people familiar with the matter.
Who Is the Suspect
The suspect has been identified as Saif al-Din Khader. He was reportedly taken into custody in Jordan on September 29, 2026.
According to Reuters' sources, Khader is working with the FBI and international law enforcement agencies to help locate other individuals allegedly linked to ShinyHunters. One source said his cooperation could play an important role in identifying and arresting more suspects.
The FBI has not publicly confirmed Khader's detention. However, the bureau said it is continuing its investigation into the recent cyber incident allegedly involving ShinyHunters and has already worked with international partners to arrest multiple suspects.
Past Links to Cybercrime Groups
Khader has previously been associated with several cybercrime communities under the aliases Rey and ReyXBF. He was reportedly one of the administrators of Scattered LAPSUS$ Hunters, a collective said to bring together members tied to Scattered Spider, LAPSUS$, and ShinyHunters.
He has also been linked to the administration of the Hellcat data-leak operation and a later version of BreachForums. Khader had earlier told journalist Brian Krebs that he had been cooperating with law enforcement since at least June 2025.
Second Arrest in the Case
The detention follows the arrest of a 24-year-old man in Amsterdam by Dutch authorities in connection with the same investigation. Independent reporting later identified him as Pepijn van der Stap, though ShinyHunters has denied any connection to him.
After the Dutch arrest, FBI Director Kash Patel said investigators were pursuing more leads and that further arrests could follow.
Growing Pressure on ShinyHunters
The group has recently been linked to several major incidents, including the alleged compromise of the FBI's FBIJobs.gov portal. ShinyHunters claimed it obtained a large volume of sensitive data related to FBI employees and job applicants. Reuters separately reported that samples of the allegedly stolen data included personally identifiable information along with sensitive employment, medical, and psychiatric details.
ShinyHunters has also been accused of breaching the website of rival cybercrime group Cl0p by exploiting a vulnerability in the Grav CMS platform.
FBI Cyber Division Assistant Director Brett Leatherman had earlier warned alleged members that investigators were continuing to identify those involved. The FBI has indicated that arrests, seized infrastructure, and cooperation from suspects could reveal more about the group's remaining members.
A Brand, Not a Single Group
Security researchers describe ShinyHunters as an evolving cybercrime brand rather than a fixed organization. Its roots trace back to earlier data-extortion communities such as TheDarkOverlord and GnosticPlayers. The ShinyHunters name surfaced around 2020 and became associated with data theft, extortion, and the trade of stolen databases.
Researchers from Sekoia and Beazley Security say the group has survived arrests, indictments, infrastructure seizures, and leadership changes by operating through a flexible network of actors.