A security vulnerability in Microsoft Outlook is reportedly being actively exploited by attackers, raising concerns about email security and credential theft.
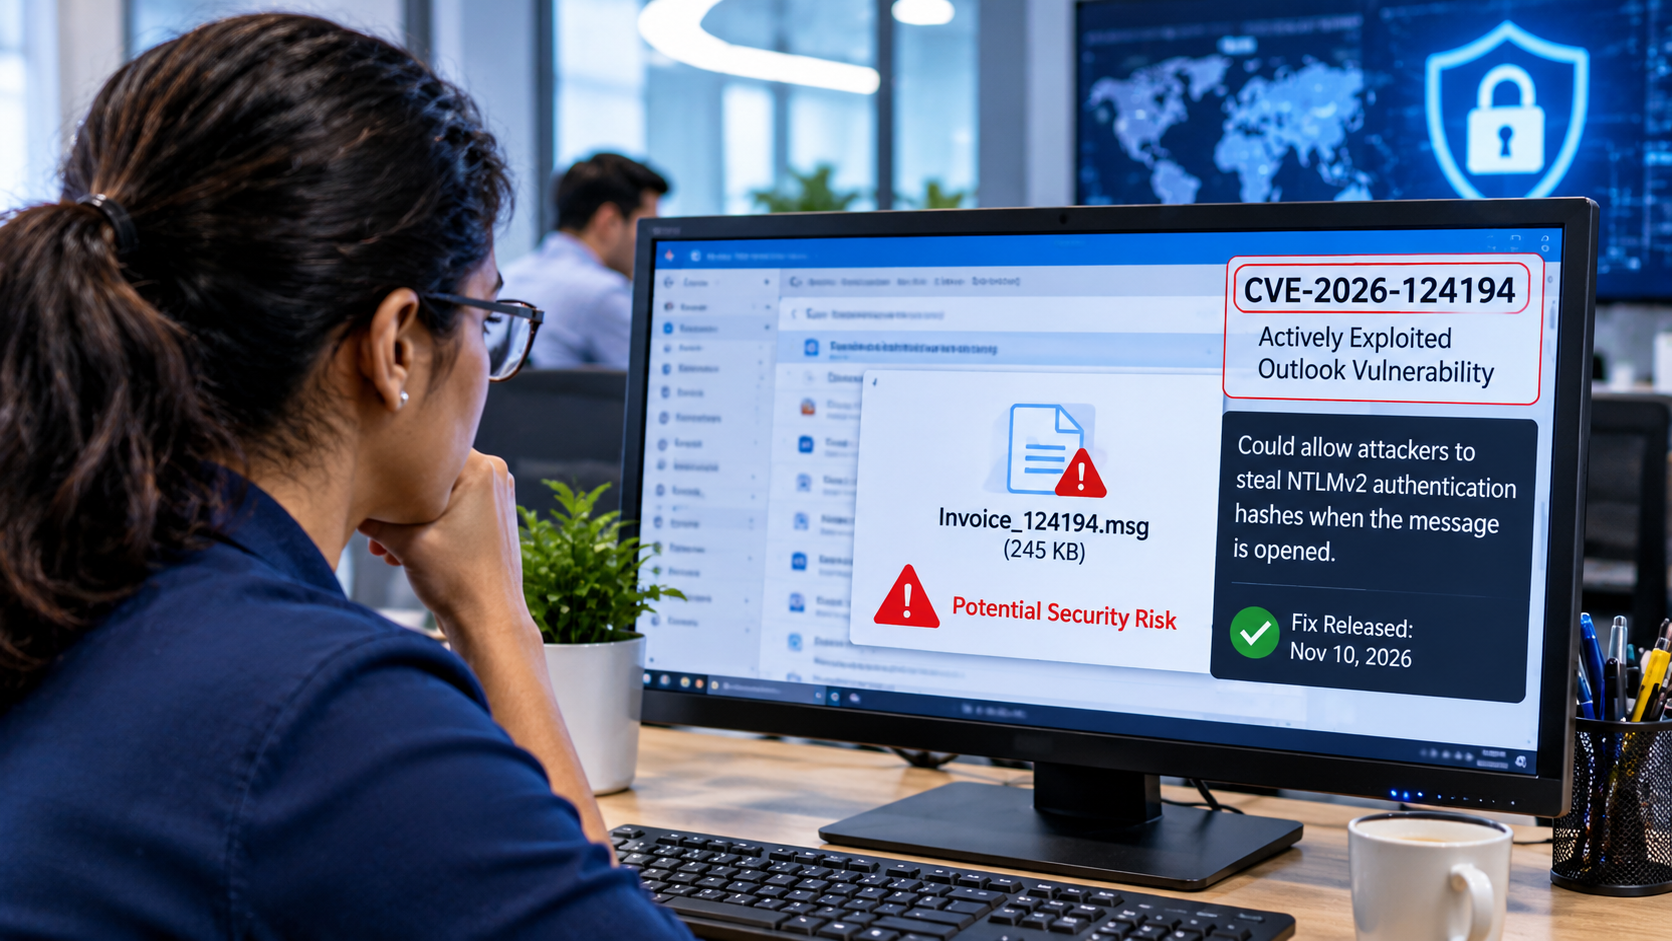
The vulnerability, tracked as CVE-2026-124194, is classified as a spoofing vulnerability. Microsoft has confirmed active exploitation, according to reporting by SecurityWeek.
The issue could allow attackers to expose a victim's NTLMv2 authentication hash through a specially crafted message file.
Microsoft released a security fix on November 10, 2026, and users are being urged to install the available updates.
Why this matters: Outlook is widely used by businesses, government organizations, and individuals. A vulnerability that exposes authentication information could create additional risks for enterprise networks.
How Does the Attack Work?
According to Microsoft's security advisory, the attack follows these steps:
- Malicious file delivery
- The attacker sends a specially crafted Outlook message file to the victim.
- Victim opens the file
- The victim is tricked into opening the malicious file in an affected version of Outlook.
- Security warning bypass
- Outlook connects to an attacker-controlled network location without displaying the usual external-content warning.
- Authentication information exposed
- The user's NTLMv2 authentication hash may be disclosed.
- Potential account impersonation
- Attackers may attempt to crack or relay the stolen hash to impersonate the affected user.
Important Technical Details
Detail
Information
Vulnerability
CVE-2026-124194
Software
Microsoft Outlook
Vulnerability type
Spoofing
CVSS score
6.5
Severity
Moderate
Exploitation
Actively exploited
Information exposed
NTLMv2 hash
Security patch
November 10, 2026
Preview Pane attack
Not supported
Microsoft's official advisory confirms that user interaction is required. Simply viewing the message in the Preview Pane does not trigger the vulnerability.
Which Microsoft Products Are Affected?
The reported affected products include:
- Microsoft 365 Apps for Enterprise.
- Microsoft Office LTSC 2021.
- Microsoft Office LTSC 2024.
Organizations should check their exact Office versions and applicable Microsoft security updates.
How Can Users Protect Themselves?
Here are some recommended security measures:
- Install Microsoft's November 10 security updates.
- Avoid opening suspicious email attachments.
- Verify unexpected files with the sender through another communication channel.
- Restrict unnecessary outbound NTLM authentication.
- Monitor suspicious authentication attempts.
- Keep Microsoft Office and Windows security updates current.
Important: Microsoft has already released a fix. Organizations should prioritize applying the relevant Office update rather than relying only on user awareness.
Impact on Cybersecurity Professionals
This vulnerability is particularly relevant to:
- SOC Analysts: Monitor suspicious authentication activity and investigate credential exposure.
- Penetration Testers: Understand NTLM authentication weaknesses and email attack surfaces.
- Security Engineers: Apply patches and strengthen enterprise authentication controls.
- Incident Responders: Investigate potential credential theft and unauthorized access